Scan the authenticator QR code safely
Scan Dosya's authenticator QR locally, protect the embedded shared secret, and confirm the six-digit setup code without exposing credentials.
Last reviewed
The authenticator QR contains the same raw shared secret shown beneath it. Anyone who copies either value can generate your future codes, so treat the setup screen like a password.

Steps
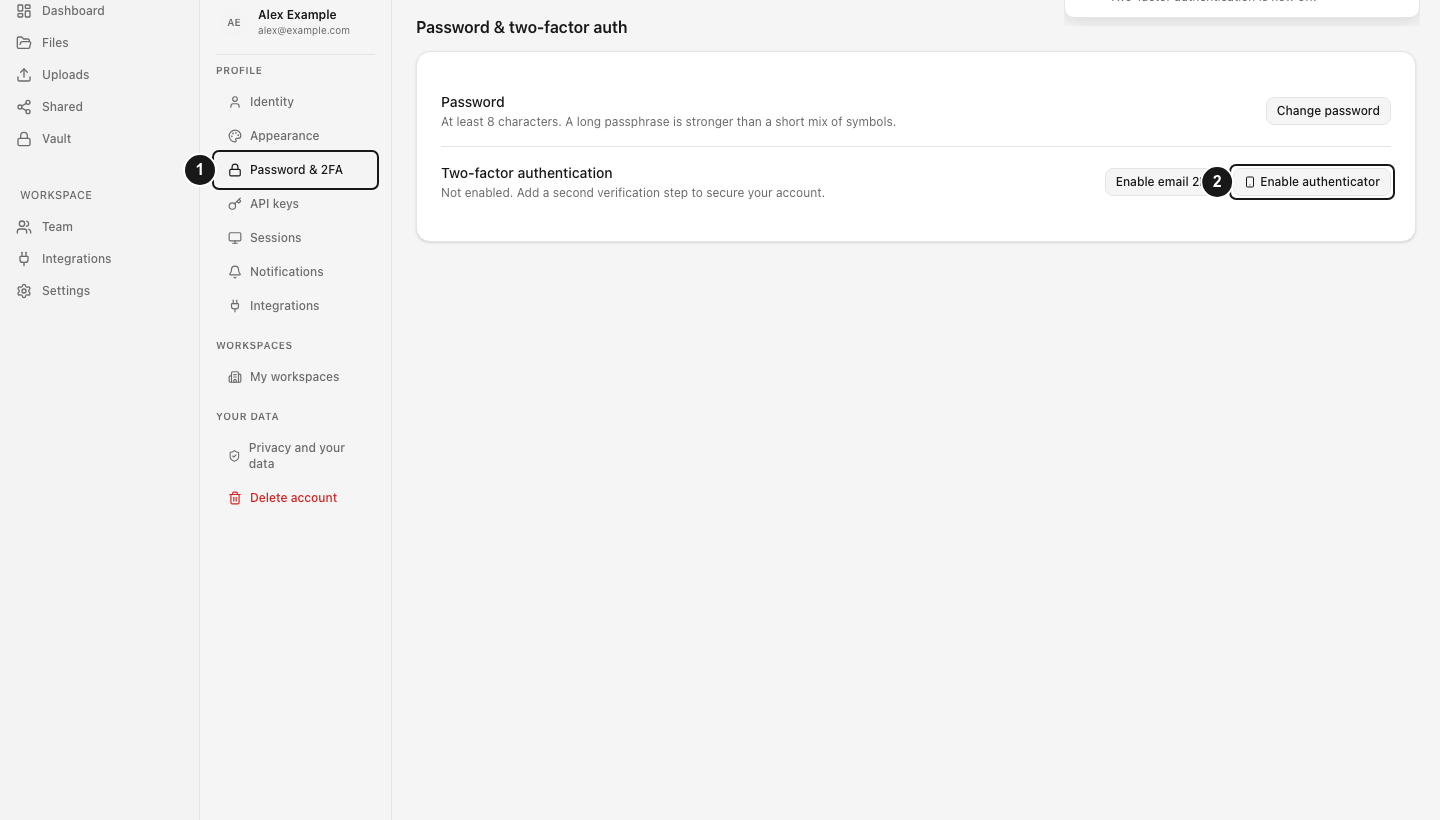
- Use a private device and open Profile → Password & 2FA → Enable authenticator.
- Dosya renders the QR inside your browser from the otpauth URI; it is not sent to a third-party QR image service.
- Scan it with an authenticator you control. If scanning fails, enter the displayed secret manually.
- Confirm that the authenticator entry identifies dosya.dev and your account email. The URI specifies SHA-1, six digits, and a 30-second period.
- Do not send the QR or secret through chat, email, tickets, or screenshots. A QR image is a reusable credential, not a one-time login code.
- Type a fresh code in 6-digit code and select Verify & enable. Dosya accepts one adjacent 30-second step on either side for clock skew.
- After the recovery codes appear, store them separately and close the modal with Done.
If you exposed the QR before confirmation, cancel and reopen setup to stage a different secret. If exposure occurred after activation, replace the factor through a controlled disable-and-enable cycle.
Expected result
The authenticator produces codes that Dosya verifies, the QR never leaves the controlled setup devices, and the settings page displays the Authenticator badge. Merely scanning without Verify & enable does not activate 2FA.
Related guides
Was this helpful?
Loading helpfulness results…
Voting saves a necessary ballot cookie for up to 180 days so you can change your answer.
Questions and replies
Ask about the steps in this guide. Questions are reviewed before publication.
Keep account details, credentials and private files out of public questions. Use private support for those.
Loading questions…
Sign in to your Dosya account to ask a question.