Review session location and IP context
Review session location and IP context with a controlled test, clear verification, limits, and recovery steps.
Last reviewed
Review session location and IP context is easier to verify when you use one controlled item and confirm the account, workspace, and destination at each step. This guide follows the current Dosya workflow and identifies the result you should see.
Before you start
- Open Profile > Security and Sessions in the current released client.
- Confirm the active account and workspace, then identify session with unexpected location information.
- Use a small non-confidential test item and record its current state before changing it.
- Keep passwords, API keys, recovery keys, private links, and personal data out of screenshots and support messages.
Steps: review session location and IP context
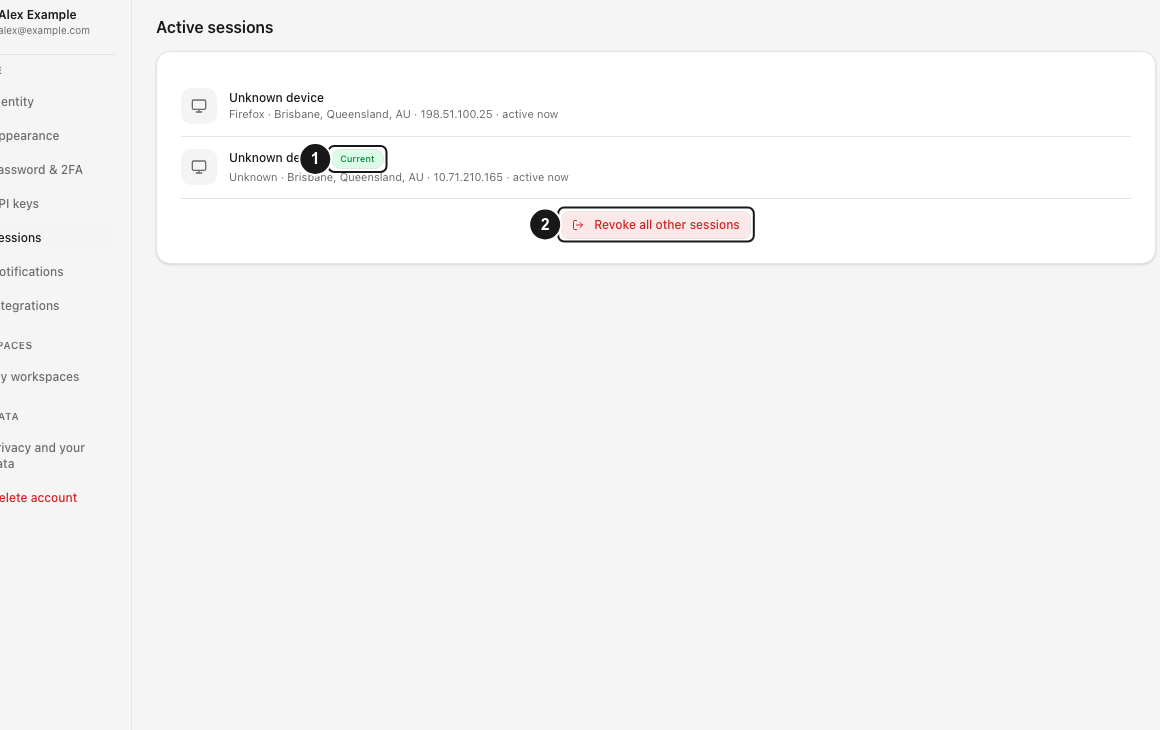
- Open Profile > Security and Sessions and confirm the active account and workspace.
- Locate session with unexpected location information and verify its name or identifying details.
- Compare the approximate location and network with VPN, mobile carrier, or travel use before deciding.
- Read the displayed warning, permission, progress, or confirmation state before leaving the screen.
- Confirm that the location is explained or treated as suspicious.
- Refresh or reopen the relevant view once to verify the result persisted.
Expected result
The controlled workflow completes and the location is explained or treated as suspicious. The result remains visible after a refresh, reconnect, or return to the relevant screen.
Limits and important details
- Available controls depend on the current client version, account plan, workspace role, and policy.
- Processing, indexing, background transfer, or third-party authorization can delay a visible result.
- For destructive, access-changing, or automation actions, validate with disposable data before applying the workflow to important files.
Troubleshooting
The expected control is missing. Return to Profile > Security and Sessions, confirm the active workspace, and check that your role and client version support the action.
The operation is rejected or stalls. Read the exact message and check permissions, locks, storage, network state, source availability, and any third-party authorization before retrying.
The result is still unclear. Repeat with one small test item, then contact support with the time, client version, workspace, and a nonsecret error or request identifier.
Related guides
Was this helpful?
Loading helpfulness results…
Voting saves a necessary ballot cookie for up to 180 days so you can change your answer.
Questions and replies
Ask about the steps in this guide. Questions are reviewed before publication.
Keep account details, credentials and private files out of public questions. Use private support for those.
Loading questions…
Sign in to your Dosya account to ask a question.