Restrict an API key to a workspace folder
Anchor a credential to one folder for WebDAV or S3, verify the mounted subtree, and understand what trashing or permanently deleting the anchor does.
Last reviewed
A folder anchor makes the selected subtree the credential’s visible root. This restriction is implemented at the WebDAV and S3 gateways, not at REST or SFTP.

Supported combination
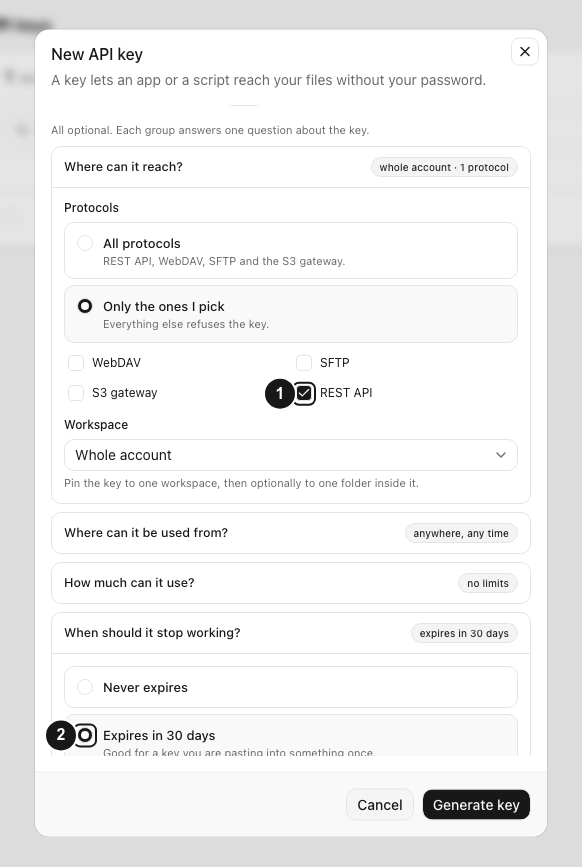
Open Profile → API keys, choose New API key, then expand Restrictions and expiry. Under Where can it reach?, select one workspace and use Choose folder…. The picker title is Limit key to a folder and its confirmation is Select folder.
Select WebDAV or S3 gateway under Protocols. The workspace role must include access_webdav for WebDAV or access_s3 for S3. Ordinary REST answers JSON with This API key is anchored at a folder and can only be used over WebDAV or the S3 gateway; an SFTP client instead reports its gateway authentication or request failure.
Steps
- Create a disposable workspace tree containing one file inside the intended anchor and another file in a sibling folder.
- In the key dialog, choose the needed operation permission, pin the workspace, select the anchor through Choose folder…, and allow WebDAV or S3.
- Generate the
dos_…secret for WebDAV. For S3, expand the saved key, choose Enable under S3 credentials, and copy the one-time Access key ID, Secret access key, Endpoint, and Region. - Confirm the member role has the matching protocol permission, then mount WebDAV or address the S3 workspace and require its root to begin at the selected folder.
- Read or write the permitted test item inside that subtree according to the chosen key permission.
- Request the sibling path and require denial, then revoke the disposable key after recording the verified boundary.
Anchor lifecycle
Scope, protocol, the current member role, locks, and other key conditions continue to apply. WebDAV returns text such as This API key is not permitted to use WebDAV or This role is not permitted to use WebDAV. S3 returns an XML AccessDenied response with the equivalent gateway or role message. A human member’s own folder confinement can narrow the credential further; an incompatible pair returns This API key is anchored outside your permitted folder.
Trashing the anchor makes WebDAV and S3 answer This API key's anchor folder is no longer available. Restoring that live folder can make its id usable again. Permanently purging the anchor or a containing subtree deletes every key anchored there and clears its REST/S3 authentication caches; that key removal is irreversible.
Moving or renaming a live anchor keeps the stored folder id, so clients see the same subtree at its new place or label rather than receiving a newly scoped credential.
Expected result
The protocol root exposes the selected folder and descendants, sibling data is unreachable, and a trashed or permanently purged anchor fails closed instead of widening access.
Related guides
Was this helpful?
Loading helpfulness results…
Voting saves a necessary ballot cookie for up to 180 days so you can change your answer.
Questions and replies
Ask about the steps in this guide. Questions are reviewed before publication.
Keep account details, credentials and private files out of public questions. Use private support for those.
Loading questions…
Sign in to your Dosya account to ask a question.