Verify an SFTP host key change
Verify a changed SFTP host key through a trusted Dosya channel, replace the saved key only after an exact match, and reconnect with confidence.
Last reviewed
REMOTE HOST IDENTIFICATION HAS CHANGED! means the key presented by the server differs from the one your client saved for that host and port. It may follow a legitimate rotation, a stale alias, or a connection to the wrong server; it can also indicate interception. Do not delete the saved record until a trusted comparison explains the change.

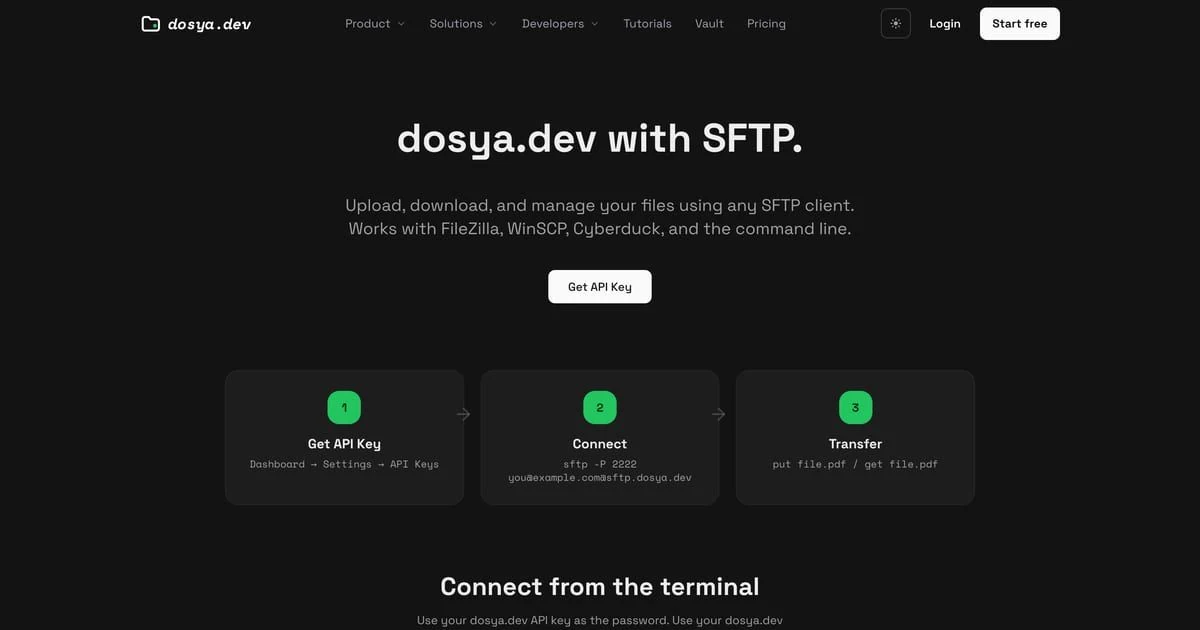
Dosya’s documented target is sftp.dosya.dev on port 2222. Known-host records for nonstandard ports are often keyed by both hostname and port, so confirm which entry the client is challenging. The repository stores server startup configuration but no certified production fingerprint.
Steps
- Cancel the connection before sending the account email’s API-key password. Save the warning text, presented algorithm and fingerprint, hostname, port, client version, and time.
- Inspect the saved site for aliases, raw IP addresses, proxies, or port 22. Correcting a wrong endpoint is safer than modifying trust for the wrong host.
- Request the current production fingerprint from Dosya support or your administrator through a channel separate from this SFTP connection. Ask whether a planned rotation occurred and which key type should be presented.
- Compare the trusted fingerprint character for character with the new value. A different algorithm or one changed character is a failed check; keep the old trust record and the connection closed.
- Only after an exact match, remove or replace the single saved entry for
sftp.dosya.dev:2222using the client’s host-key manager. Do not clear the entire known-host database or enable automatic trust. - Reconnect, verify the prompt now shows the confirmed key, authenticate with the dedicated API key, and perform a read-only workspace listing. Report any second change immediately.
Changing the SSH host-key record has no effect on API-key validity, scope, workspace pin, or role permissions. Conversely, revoking an API key does not update the SSH trust record. These are independent identity checks.
Do not send your dos_… secret, complete client configuration, or private known-host database to support. The old and new public fingerprints, algorithm, endpoint, timestamp, and client name are enough for the verification decision.
Expected result
The saved trust entry changes only after the new fingerprint matches a separately confirmed Dosya value. The following connection reaches sftp.dosya.dev:2222, presents that verified key, and completes a harmless workspace listing.
Related guides
Was this helpful?
Loading helpfulness results…
Voting saves a necessary ballot cookie for up to 180 days so you can change your answer.
Questions and replies
Ask about the steps in this guide. Questions are reviewed before publication.
Keep account details, credentials and private files out of public questions. Use private support for those.
Loading questions…
Sign in to your Dosya account to ask a question.